Recommended Starting Points
These are the fundamental guidance articles to start with - scroll down for more specific guidance and related content




Introductory Level
The consequences of failing to plan properly for new security projects or upgrades of existing security measures can be costly.
Guidance on how to take a security-minded approach to Digital Engineering, Technologies, Projects and Initiatives
This guidance is for early-stage investors in emerging technology companies.
Guidance for business who are also suppliers on how to develop and improve their security profile. This aims to encourage suppliers to see security as part of their competitive edge.
Guidance for those practitioners responsible for implementing supply chain security within organisations. Suitable for procurement professionals, commercial teams, security professionals, and others.
High level guidance for senior business leaders on protecting business from supply chain attacks. This aims to empower to prioritise and resource supply chain security.
High level guidance for senior business leaders on protecting business from supply chain attacks. This aims to empower to prioritise and resource supply chain security.
Consider security early when seeking investment to protect your company and help you prepare for the National Security and Investment Act
Protected Procurement is guidance for businesses and organisations to help embed security across supply chains and to protect from supply chain attacks. Created in partnership with CIPS
If implemented early enough, mitigations will be a necessary part of risk management when doing business with overseas parties.
It is important that you understand the risks associated with deploying these technologies, whether they relate to location sensitivities, data protection considerations or privacy concerns
Developing a risk based plan to doing business with overseas parties is essential to ensure success.
Guidance on a security-minded approach to securing underground asset data.
Being aware of government’s business screening requirements will allow you to be mindful of any national security threats.
Good governance and proactively considering security in business plans with overseas parties sets the tone of your risk appetite.
If taken in a timely manner, practical steps to manage risks will protect your reputation, prosperity and the national security of the UK.
Secure Business, an open approach to international business and engagement to protect your long-term profitability, reputation, and the UK's national security
10 important steps organisations can take to enhance personnel security measures to mitigate insider risk
Intermediate Level
This guidance presents an overview of the principles behind Vehicle As a Weapon (VAW) detection, the different technologies available & considerations regarding the environments in which they may operate
The guide helps risk owners, and their security advisors, to understand and manage the risk to building occupants, people outside the building and other assets resulting from damage to building facades caused by the blast effects of an external improvised explosive device (IED)
NCST are highly functional computers which are connected to a network and need to be suitably protected
Data centres operators and their customers should both have individual risk management strategies designed to protect their critical assets and systems.
Data centres operators and their customers should both have individual risk management strategies designed to protect their critical assets and systems.
This guidance note is to assist the building owner, security manager and facility managers to ensure that suitable bullet resistant glass is selected to mitigate the threat and that have been certified as meeting the required standard
This document supplements the NPSA Standard by providing a method for testing external doors, non-glazed panels and non-loadbearing walls under blast loading from external IEDs and assessing the damage and hazard to people
NPSA recommends that products required to protect against a firearms attack are tested at an accredited test centre in accordance with the BS EN standards
This guidance note is to assist the building owner, security manager and facility manager in selecting a design threat and ensuring that suitable products are used to mitigate the threat
This guidance note is to assist the building owner, security manager and facility managers to ensure that suitable bullet resistant glass (BRG) is selected to mitigate the threat and that have been certified as meeting the required standard
Guidance note on measures to improve the blast resistance of glazing
A summary of the different types of curtain walling systems that exist and where these are typically used
This guidance supplements existing Security Minded Communications guidance and provides tailored advice for UK organisations which have remote or rural locations as part of their estate in the UK.
Assess your organisation’s personnel security maturity to build resilience
Protective security is important for a site’s own infrastructure which is crucial for it to function or could present hazards if attacked.
Data centres operators and their customers should both have individual risk management strategies designed to protect their critical assets and systems
Consider how contract staff may pose the same, or differing, security risks and how to manage these risks
An introduction for Local Authorities, Event organisers, and similar end user groups on using temporary Vehicle Security Barriers (VSBs) as part of a HVM scheme - which itself should be one piece of a wider security plan.
Advanced Level
The planning process has a key role in making places – recommending how and where buildings should be built, what they should be used for and how they should fit into the local surroundings.
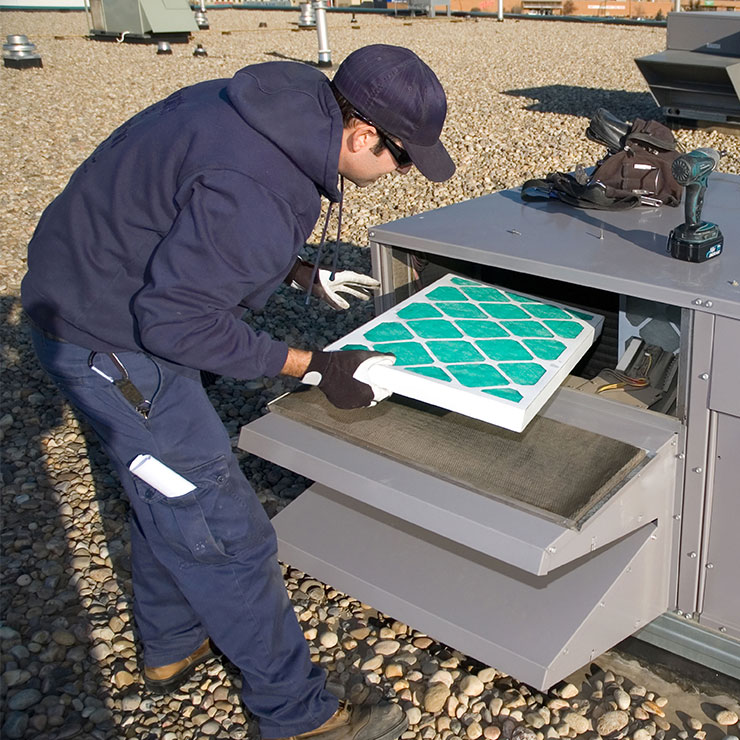
HVAC systems may provide a viable, rudimentary means of dispersing chemical or biological agents. Measures to reduce this risk may need to be considered

Guidance to provide high level, practical advice to anyone looking to formulate a Site Security Plan, assisting in developing a proportionate plan which aims to mitigate Terrorist and State threats, whilst supporting in countering many other types of security or safety threats.
NPSA have developed this guidance as we often see security being considered too late in the design process where the physical security measures conflict with the design aspirations

Windows and glazed facades are important elements of a building that can be vulnerable to forced entry, ballistic, surreptitious and other attacks
All Levels
Guidance to help those responsible for an organisation or site’s security to procure effective detection dog services that meet their security needs
Supporting our customers in assessing and mitigating the security risks posed by uncrewed aerial systems (UAS), also known as UAV or drones
Developing Operational Requirements for C-UAS Detect, Track and Identify Technology
How to assess the vulnerability of a site to the threat of Uncrewed Aerial Systems (UAS)
A key purpose of connected places, also known as smart cities, also known as is to join up specific vertical sectors across organisational boundaries into a whole-city approach for the creation, delivery and use of city spaces and services
PAS 185:2017 Specification for establishing and implementing a security-minded approach
PAS 185:2023 is a specification for establishing and implementing a placewide, strategic-level, security-minded approach as part of both its development and operation
This guidance provides the questions which an organisation needs to ask of itself and its supply chain, including its professional advisers, in order to gain an understanding of what information it, or others, holds in relation to its built assets
An introductory guide for built asset owners and facilities managers
This guidance document is intended for use by managers leading and teams delivering digitalisation initiatives. It sets out a process to determine high-level information need and any associated security and management requirements
Guidance on how to take a Security-Minded approach to Digital Engineering, Technologies, Projects and Initiatives
This short document illustrates a ‘4 Step Publication Approach’ aimed at helping those preparing documents for electronic publication to a wide community, including publicly accessible websites and document servers
A Security Considerations Assessment (SCA) is a structured process for identifying and managing security risks associated with an activity
This guidance lists the key UK legislation, regulations and codes that decision-makers responsible for connected places should be aware of when collecting, storing, processing, generating or sharing data and information relating to connected place services and built assets
A specification for security-minded building information modelling, digital built environments and smart asset management
A specification for security-minded building information modelling, digital built environments and smart asset management
Guidance to aid those responsible for developing, designing, and delivering a new perimeter solution
Guidance on supply chain resilience or the security of supply. Aims to help businesses and organisations to anticipate, prepare and adaptively respond to prevent disruption to supply chains.